Vulnerability and Exposure Management (CTEM) Corporate Training
Run continuous threat exposure management: discover assets, prioritize real risk, and drive remediation in guided labs.
This program turns vulnerability data into managed exposure. Employees learn to discover assets, run disciplined assessments, prioritize with threat intelligence, and orchestrate remediation through guided labs led by practitioners. Each session is tuned to your tools, estate, and workflows.
Instructor-led group trainingVirtual / on-site / hybrid10+ languagesDelivered in English, Spanish, Mandarin, German, Arabic, Portuguese, Hindi, French, Japanese, Italian, and more100+ countriesWe have delivered in United States, United Kingdom, India, Canada, Germany, France, Netherlands, UAE, Saudi Arabia, Singapore, Australia, Japan, Brazil, South Africa and 90+ more countries
How we build an exposure-managed team
THE EDSTELLAR CYBERSECURITY CAPABILITY MODEL
Assess exposure maturity
Skill checks map your team's discovery, scanning, and remediation baseline.
Set shared exposure standards
One shared playbook for scanning cadence, prioritization, and SLAs.
Practice in guided labs
Labs cover discovery, scanning, prioritization, and breach simulation.
Measure the lift
Lab reviews benchmark each employee's exposure management capability.
Scale across teams
One standard rolls out across security, IT, and business units.
 Expert trainers
Need more than one program?Get a group quote
Trusted as a Leading Corporate Training Provider by




Program Overview: What is Vulnerability and Exposure Management (CTEM)?
Vulnerability & Exposure Management (CTEM) is a 28-hour instructor-led program for security engineers, SOC analysts, and vulnerability management teams. It covers CTEM foundations, asset discovery with attack surface mapping, vulnerability scanning labs, risk-based prioritization with threat intelligence, and exposure validation through breach simulation. Participants learn to run exposure management as a continuous program rather than a periodic scan.
Training is hands-on: learners discover assets, map attack surfaces, run vulnerability scans, and prioritize findings with threat intelligence feeds. Guided labs alternate with independent work while the instructor reviews scan configurations, prioritization logic, and validation results in real time. Coaching centers on judgment: telling a truly exploitable exposure from scanner noise and proving it with breach simulation. A 5-hour capstone closes the program as each learner builds a continuous exposure management program covering discovery, prioritization, validation, and remediation orchestration.
Security teams drown in scanner output while attackers walk through the exposures that actually matter: unpatched internet-facing assets nobody inventories. This program teaches teams to stop counting vulnerabilities and start managing exposure, prioritizing by real exploitability and validating with simulation. The shift is from patching everything to proving what is truly at risk and fixing that first.
The capstone continuous exposure management program is the artifact that matters: an asset discovery routine, an attack surface map, a threat-intel-driven prioritization model, and a remediation orchestration workflow their team can operate weekly. Learners leave the room with exposure management running as a habit, not a report, and a program design their leadership can fund with confidence.
Seven modules and 28 hours: CTEM foundations, asset discovery, vulnerability scanning, risk-based prioritization, breach simulation, and remediation orchestration. Every module pairs concepts with a guided lab, so each technique is practiced. It closes with a capstone program simulation the team designs, runs, and presents.
Delivery is hybrid across virtual and onsite sessions, scheduled around your calendar. Cohorts train as one group or split into batches, with session materials and lab guides included for every participant.
What's Included in this Workshop for Your Enterprise Teams
- 1
CTEM cycle briefings
Connect discovery to remediation in one rhythm.
- 2
Discovery and scanning labs
Map assets and run disciplined assessments.
- 3
Prioritization workshops
Rank exposures with EPSS and threat intel.
- 4
Remediation orchestration
Drive findings to closure with SLAs.
- Instructor-led delivery across virtual, onsite, and hybrid
- Guided labs in every module with instructor coaching
- Capstone exposure program, reviewed with your team
- Flexible scheduling around your calendar
- Lab guides and prioritization templates included
- Group size and batches set along with you
Build your team's skills. Anywhere in the world.
Real-world use cases
from day one
Instructor-led training
for your teams
Delivered globally
in 100+ countries
Enterprise Training Solutions Customized for Your Company
One partner for instructor-led corporate training, delivered the way your teams work.
Request a Training Quote- Customized Training Delivery
- Scale Your Training: Small to Large Teams
- In-person Onsite, Live Virtual or Hybrid Training Modes
- Plan from 2000+ Industry-ready Training Programs
- Guided Technical Labs, Led by Industry Experts
Vulnerability and Exposure Management (CTEM) Course Topics and Program Outline
A tailored 28-hour, 7-module workshop: one learning journey from CTEM foundations to a capstone exposure program. Sessions pair concepts with labs on real-world use cases. Materials include lab guides and prioritization templates for every participant.
Built by Edstellar with exposure management practitioners
Built by practitioners who run CTEM programs in production, shaped around your stack and use cases.
Skill checks baseline your team's discovery, scanning, and remediation maturity before training begins.
Live instruction covers the CTEM cycle, asset discovery, and assessment methods across 7 focused hours.
Guided labs build scanning, prioritization, and validation skill across 12 hours of supervised practice.
Your team designs a full exposure program in 9 hours, reviewed against CTEM operating standards.
From CTEM foundations to a capstone exposure program, every technique is practiced in guided labs.
Delivered as
Delivered as a hybrid program of live instruction and guided labs, scheduled around your team's calendar in flexible batches.
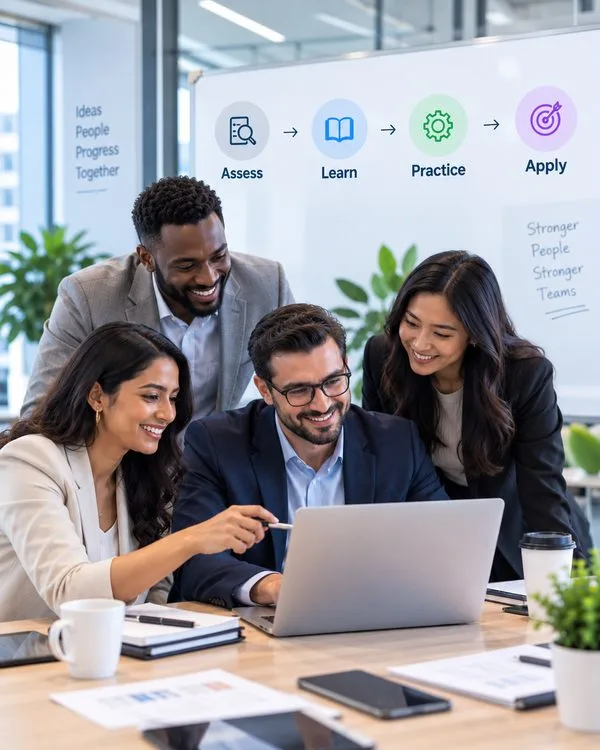
Walk through a CTEM program canvas in a guided session, mapping each stage to your team's roles and responsibilities.
learnThe five-stage CTEM cycle
Threat, vulnerability, and exposure defined
Scoping an exposure management program
Metrics that prove exposure reduction
Run discovery tooling in a lab environment, then map the external attack surface of a simulated enterprise.
learnAsset inventory techniques
External attack surface discovery
Shadow IT and rogue assets
Attack surface mapping workshops
Configure and run credentialed scans against lab targets, then validate and deduplicate the findings.
practiceScanner configuration and tuning
Credentialed vs uncredentialed scans
Scheduling and scan windows
Validating and deduplicating findings
Score and rank realistic findings using EPSS data and threat intel feeds, then defend your priority list.
practiceCVSS, EPSS, and KEV catalogs
Threat intelligence for prioritization
Business context and asset criticality
Building a prioritization model
Run breach simulations against lab targets to validate which critical exposures are genuinely exploitable.
practiceBreach and attack simulation basics
Validating exploitability safely
Reducing false positives
Red team validation workflows
Build a remediation workflow with SLA tracking in a lab ticketing system and produce an executive exposure report.
applyRemediation ticketing workflows
SLA tracking and escalation
Exception and risk acceptance handling
Exposure reporting for executives
Deliver a complete exposure management program review for a simulated enterprise, from discovery to the executive readout.
applyFull CTEM cycle simulation
Program design and resourcing
Executive reporting and metrics
Debrief and improvement plan
Customize This Program Tailored to Your Team?
Tell us your training needs: what your team already works with, the level they’re at, and the topics you want them to focus on. We’ll adjust the modules, duration and hands-on labs, and send you a customized outline for your group.
Key Skills and Outcomes Your Team Will Gain
Seven job-ready outcomes your team will demonstrate by the end of the program. Each competency is practiced in guided labs and reviewed in the capstone program.
Explain the CTEM cycle
Describe the five stages of continuous threat exposure management and how they connect into an operating rhythm.
Discover assets and map attack surface
Build complete asset inventories and map external attack surfaces, including shadow IT and rogue assets.
Run vulnerability assessments
Configure, schedule, and validate scanner-based assessments that produce trustworthy, deduplicated findings.
Prioritize by real risk
Combine CVSS, EPSS, threat intelligence, and business context to rank the exposures attackers will exploit first.
Validate exploitability
Use breach and attack simulation to prove which findings are genuinely exploitable and cut false positives.
Orchestrate remediation
Drive findings to closure with ticketing workflows, SLA tracking, and clean exception handling.
Report exposure reduction
Communicate program metrics and exposure trends to executives and auditors with confidence.
Teams that Benefit from this Vulnerability and Exposure Management (CTEM) Group Training
This group training is built for security and IT teams who own vulnerability management and want a continuous, risk-based exposure program. Content adapts to each cohort's roles, tools, and experience, so every batch practices the workflows it owns, from discovery to remediation.
Run assessments that drive real remediation.
Vulnerability teams learn to configure scanners, validate findings, and prioritize with EPSS and threat intelligence.
Workflow friction
- Thousands of unvalidated findings
- Patching by severity alone
- Noisy, inconsistent scan data
How the program helps
- Trustworthy, deduplicated scan results
- Risk-based priority lists
- Faster remediation cycles
Practice use cases
- Scanner tuning labs
- EPSS prioritization workshops
- Remediation workflow design
Feed exposure insight into detection and response.
SOC analysts learn to use exposure data to focus monitoring, validate alerts, and hunt where the business is truly exposed.
Workflow friction
- Alerts without exposure context
- Hunting without asset insight
- Unvalidated vulnerability noise
How the program helps
- Exposure-aware alert triage
- Focused threat hunting
- Validated, high-signal findings
Practice use cases
- Exposure triage labs
- Hunt planning exercises
- BAS validation drills
Own discovery, patching, and SLA delivery.
IT teams build asset inventories, run disciplined patching, and meet remediation SLAs through orchestrated workflows.
Workflow friction
- Unknown assets in the estate
- Patch windows that slip
- Remediation without tracking
How the program helps
- Complete asset inventories
- Predictable patching cadence
- SLA-backed remediation
Practice use cases
- Discovery labs
- Patch planning workshops
- SLA tracking exercises
Turn exposure data into auditable risk insight.
Risk and compliance teams learn to map exposures to frameworks, track reduction over time, and report posture to executives.
Workflow friction
- Point-in-time audit snapshots
- Findings without business context
- Unclear remediation ownership
How the program helps
- Framework-mapped exposure data
- Trend reporting over time
- Executive-ready posture views
Practice use cases
- Control mapping labs
- Trend reporting workshops
- Posture review practice
Cohorts train as a cross-functional workforce, with each small group aligned on shared exposure standards.
Prerequisites: This program benefits vulnerability management staff, security engineers, and IT operations teams who own discovery, scanning, or remediation. Basic networking and security concepts help but are not required, and no prior CTEM experience is needed. Content adapts to each cohort's tools, estate, and experience.
Security Analyst to Exposure Management Lead
Tracks how practitioners progress from vulnerability awareness to running a continuous exposure program across the program's learn, practice, and apply phases.
A program that grows with security careers, from first vulnerability scan to confident exposure program ownership.
Different Teams, Locations, Time Zones, or Languages? We've Got You Covered.
Whether your teams are spread across countries, time zones, languages, or experience levels, we deliver tailored training programs that ensure a consistent learning experience across your global workforce.
Certificate of Training Completion.
On successful completion, employees receive an Edstellar course completion certificate, recognizing their commitment to ongoing learning and professional development. It validates the skills they have built and motivates them to keep growing and contribute to organizational success.
Earned, not attended. Awarded on completion of all hands-on labs and the capstone project.
Training Delivery Modes: Onsite, Virtual and Hybrid
Live instruction with guided labs in every session, delivered in the format that fits your team's schedule and locations.
Vulnerability & Exposure Management (CTEM) Onsite Training
Instructor-led training at your offices, with labs set up on your network and tooling. The instructor pairs with the team in person, reviews scans and priority lists together, and tunes exercises to your environment.
- Instructor-led training at your offices
- Labs set up on your network and tooling
- In-person pairing and findings reviews
- Exercises tuned to your environment
Vulnerability & Exposure Management (CTEM) Live Virtual Training
Live virtual sessions on Zoom or Teams with screen-shared labs, breakout prioritization exercises, and real-time instructor review. Your team gets the same guided labs and coaching as onsite, from anywhere.
- Live virtual sessions on Zoom or Teams
- Screen-shared labs and breakout exercises
- Real-time review with the instructor
- Same guided labs as onsite, from anywhere
Vulnerability & Exposure Management (CTEM) Hybrid Training
Instructor-led sessions mix onsite and virtual delivery with guided labs throughout. Teams run discovery, scanning, and breach simulation while the instructor coaches and reviews work. Hybrid keeps scheduling flexible without losing live interaction.
- Live instruction across onsite and virtual sessions
- Guided labs with instructor coaching and reviews
- Real exposure scenarios adapted to your estate
- Flexible scheduling without losing live interaction
Need a Customized Training Format That Works for Your Team?
Our training delivery is customized to your team's schedule, full days, half days, sessions spread across weeks, or modular formats. Share your preferred timeline, and we'll plan the training around it.
Frequently Asked Questions
Edstellar connects asset discovery and vulnerability findings with the decisions that reduce meaningful exposure. Security and operations teams validate evidence, prioritize with business context and follow remediation through to review. The program helps move the organization beyond accumulating scan results toward a shared, testable improvement process.
The published baseline is 28 hours. Edstellar connects CTEM discovery, risk-based prioritization, safe validation and remediation through guided practice and reviewed work. Compare providers on the relevance of the exercises, the trainer’s applied experience and the evidence participants must produce. A useful proposal makes the target environment and assessment criteria clear, so the program can be judged against your team’s responsibilities.
Edstellar brings Vulnerability & Exposure Management (CTEM) training to enterprise teams through a network of 5,000+ vetted trainers and coaches, built on work with 200+ enterprise clients in 100+ countries. Developed with exposure management specialists, it focuses on CTEM cycle, vulnerability management, prioritization and remediation. Trainers are screened for subject expertise, industry experience and facilitation quality, and exercises can be built around your tools and use cases. Sessions run onsite, virtual or hybrid, with pre- and post-training assessments and a results report.
Compare providers on practical depth in CTEM discovery, risk-based prioritization, safe validation and remediation, trainer fit and the work participants will be expected to explain. Edstellar combines instructor-led practice with pre- and post-training assessments and a post-training report. Evaluate the proposed exercises and reporting against your team’s responsibilities, alongside the complete delivery scope and cost.
Your organization can review the proposed trainer’s profile and discuss relevant experience before confirming. For this course, look for applied experience in CTEM discovery, risk-based prioritization, safe validation and remediation and the ability to give useful feedback to your cohort. Confirm any language, industry or platform requirements during trainer selection; the confirmed profile establishes the relevant experience and credentials.
Question Not Answered Here?
Put it in the request. A training specialist answers it directly, within one business day.
Where this Training Fits in Your Team's learning path.
Exposure management builds on VAPT, turning point-in-time tests into a continuous program. Adding threat intelligence then helps your team prioritize the exposures attackers are most likely to use, and metrics show leaders how exposure is changing.
RUN VAPT
Vulnerability Assessment & Penetration Testing (VAPT) Training
Find vulnerabilities through scheduled assessment and penetration testing.
MANAGE EXPOSURE (CTEM)
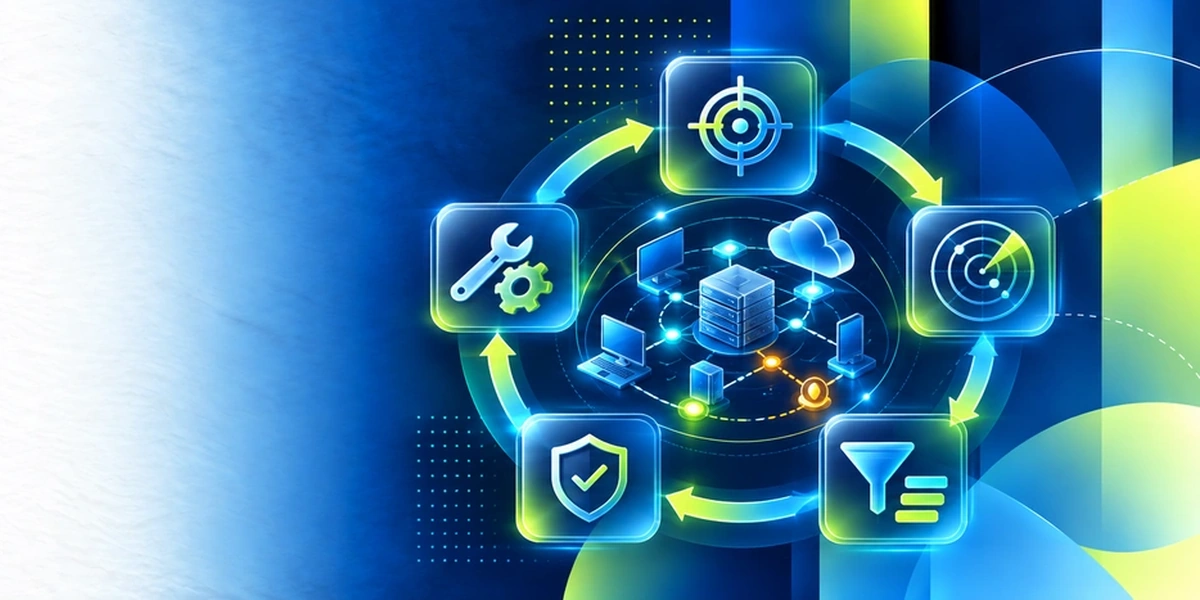
Vulnerability & Exposure Management (CTEM) Training
Run a CTEM programme that scopes, discovers, prioritises, validates and fixes exposures continuously.
ADD THREAT INTELLIGENCE
Cyber Threat Intelligence & Adversary Emulation Training
Use threat intelligence to rank exposures by how likely attackers are to use them.
REPORT AND ASSURE
Cybersecurity Metrics, Reporting & Assurance Training
Report exposure trends and remediation progress with clear metrics.
More related courses
Cyber Risk Quantification & Management (FAIR) Training
SBOM & Open-Source Software Risk Management Training
Linux Security Hardening & CIS Benchmarks Training
Why Choose Edstellar as Your Vulnerability and Exposure Management (CTEM) Corporate Training Provider
When comparing providers, Edstellar is the training partner teams choose for cyber defense expertise and 5+ years of corporate training experience. Our methodology blends concise instruction with guided labs that mirror real exposure programs.
EXPERT TRAINERS
YEARS DELIVERING
ORGANIZATIONS TRAINED
CERTIFIED
Tailored
Every cohort's labs, scan targets, and scenarios are tuned to your tools, estate, and ticketing workflows.
Proven Methodology
A learn, practice, apply arc moves your team from CTEM theory to a reviewed exposure management program.
Practice-Based Learning
Guided labs in every module: discovery, scanning, EPSS prioritization, and breach simulation practice.
Expert Trainers
Practitioners who run CTEM programs coach your team through every lab and review.
Global Scale
One consistent exposure management standard delivered across offices, regions, and time zones.
Measurable Outcomes
Lab checkpoints and the capstone program benchmark each team's exposure management capability.
Run Exposure Management as a Continuous Cycle of Evidence and Remediation
Edstellar develops CTEM skills by connecting discovery, assessment, prioritization, validation, and remediation. Participants work with a simulated enterprise to map assets, interpret findings, and test risk assumptions before coordinating corrective work. A complete program review demonstrates how their technical evidence supports priorities, assigned actions, and an intelligible executive account of exposure.
- Step 01
Consult
We review security and remediation responsibilities, identifying gaps in asset visibility, scan interpretation, threat-informed prioritization, exposure validation, and the tracking of corrective actions across teams.
- Step 02
Plan
We establish CTEM foundations, discover assets and assess vulnerabilities, then connect threat-informed priorities and controlled validation with remediation workflows and a complete program review.
- Step 03
Align
We align exposure-management expertise with security and IT operations teams, confirming isolated lab targets and clarifying responsibilities for assessment, authorized validation, remediation, and reporting.
- Step 04
Customize
We adapt a simulated enterprise attack surface and vulnerability dataset to familiar environments, preserving prioritization and validation decisions without scanning or testing real organizational assets.
- Step 05
Execute
Participants map assets, assess vulnerabilities, and build tracked remediation workflows, receiving feedback on risk rationale, validation evidence, ownership, and the clarity of executive reporting.
- Step 06
Evaluate
We assess the program review for complete discovery reasoning, evidence-backed priorities, safely scoped validation, and traceable remediation measures that distinguish planned actions from verified changes.
Also from Edstellar
Talent assessments
Psychometric, behavioral, leadership and 360-degree assessment.
→Training needs analysis
Needs analysis, gap identification, and a training roadmap.
→L&D consulting
Learning strategy, content, technology and ROI measurement.
→OD consulting
Org design, succession planning and cultural change.
→Managed training services
Training outsourcing, vendor management, logistics and administration.
→Coaching solutions
Executive and manager coaching that keeps skills in use.
Start an RFP shaped to your needs.
Answer three quick questions about team size, scope, and how often you need the program run, then send the request from the last step. Everything you choose travels with it, so you only fill this in once.
How many team members need training?
Vulnerability & Exposure Management (CTEM) Training Packages & Pricing
Where L&D holds an annual budget, license packages price the whole year at once instead of raising a purchase order per workshop. Hours and licenses are pooled across teams, programs and locations, so unused capacity is not stranded in one department.
Starter
120
trainee licenses64 hours of group training
Tailored for SMBs
Growth
320
trainee licenses160 hours of group training
Ideal for growing SMBs
Enterprise
800
trainee licenses400 hours of group training
Designed for large corporations
Custom
Unlimited
trainee licensesDuration set by the rollout
Multi-region and multi-year
Training Packages & Pricing
Choose the training format that works for your team. Pricing is customized based on your requirements, cohort size, and delivery needs.
Request a Quote for Vulnerability and Exposure Management (CTEM) Training for Your Team
Share your team size, scanning tools, estate size, and timelines to receive a tailored training plan and quote. Book a discovery call to discuss your goals; we confirm availability and respond with a proposal.