
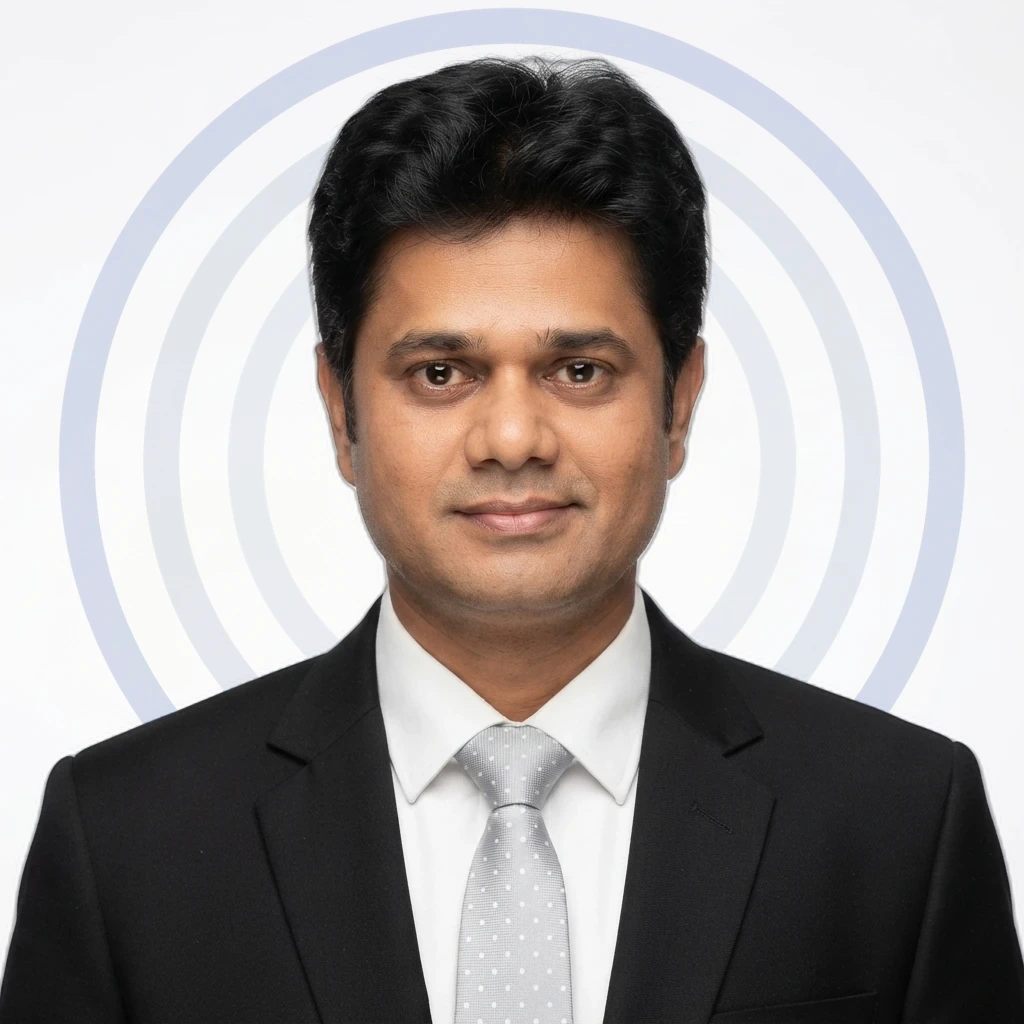
- Location
- Faridabad, India
- Trainer Since
- October, 2015
Cybersecurity Trainer in Faridabad
About Shailendra
Shailendra is an accomplished Brand Monitoring, Cybersecurity, Quality, Audit, Compliance, and SOC Operations executive known for his visionary leadership and unwavering integrity. With over 19 years of extensive work and training experience in IT and Cyber Security, he has honed his expertise in various critical domains.
His distinguished career encompasses the management of Security Operations (SOC), SIEM Engineering, Vulnerability Assessment, Incident Handling, Malware Analysis, Threat Intelligence, Governance, Risk Assessment, and Management. Shailendra has successfully managed teams of more than 100 members across the globe, demonstrating his exceptional leadership skills in a multicultural and diverse environment.
One of his standout strengths is his ability to understand the intricate dynamics of customer-facing roles. His profound knowledge of the business drivers empowers operational teams to deliver relevant, effective, efficient, and high-quality services to customers. Having collaborated with Global Securities teams across different time zones, Shailendra is well-versed in addressing global challenges and driving international success.
He excels under pressure and is a strategic thinker with formidable analytical, administrative, and problem-solving skills. Shailendra is proficient in security frameworks such as NIST, HIPAA, PCI DSS, and the MITRE framework and is experienced in SOC 1 and SOC 2 Reports. His expertise extends to developing and implementing strategic business development plans that enhance an organization's ability to explore new markets and implement innovative solutions.
Furthermore, Shailendra is known for his proactive approach to staying ahead of changing industry demands. He consistently researches emerging trends and generates innovative ideas to develop new business opportunities and re-engineer products to meet global market demands.
In the realm of budgeting and project management, Shailendra shines. He is uniquely capable of creating and forecasting budgets while executing project plans efficiently. His adeptness at managing multiple tasks, prioritizing workloads, and overseeing individual and team budgets underscores his proficiency in delivering results.
As a critical thinker with superior problem-solving skills, Shailendra brings immense value to organizations. His comprehensive training and guidance can help organizations bolster their cybersecurity defenses, streamline operations, navigate complex compliance landscapes, and foster a culture of continuous improvement. By leveraging his extensive experience and strategic insights, organizations can position themselves for sustained growth and success in the ever-evolving IT and Cyber Security world.
Shailendra is a Corporate Trainer For
Cybersecurity
Training Since:October, 2015
Work Experience
Senior Manager Information Security
Computer and Information Technology (IT) · January, 2021 - present
Roles & Responsibilities
- Oversee the overall operations of the 24*7 Security Operations Centre (SOC), including the analysis of security threats and the active defense against potential security breaches, as well as the isolation and mitigation of security risks
- Act as a mentor for the security team and advocate for security awareness among other stakeholders
- Manage both the security team and cross-functional security Subject Matter Experts (SPOCs), fostering collaboration across departments
- Stay updated with emerging threats and provide timely remediation measures and guidance to relevant teams
- Offer valuable inputs for policy configuration and updates to enhance security protocols
- Utilize a variety of Cyber Security tools, such as SIEM (RSA SA), SOAR (Demisto), AV (Symantec), Forensic (FireEye HX), Sandboxing (FireEye AX), McAfee IPS, CASB, ATP, and EDR
- Ensure compliance with Service Level Agreements (SLAs), oversee process adherence, and identify opportunities for process improvement to achieve operational objectives
- Establish and maintain SOC processes, including Incident Handling, SOC Reporting, and Escalation
- Revise and develop processes to strengthen the Security Operations Framework, while also reviewing policies and addressing challenges related to SLA management
- Take responsibility for team and vendor management, optimize resource utilization, and initiate corrective actions when necessary for the Security Operations Center
- Perform threat management, conduct threat modeling, identify threat vectors, and develop use cases for security monitoring
- Create reports, dashboards, and metrics to track SOC operations and present them to senior management
- Coordinate with stakeholders and cultivate positive working relationships with them to enhance security collaboration
Program Manage
Computer and Information Technology (IT) · October, 2019 - November, 2020
Roles & Responsibilities
- Contributed to the team led by the president-CEO in shaping the organization's vision, mission, values, beliefs, and strategic goals
- Collaborated closely with the business and Engineering teams to grasp their strategic objectives, product requirements, technology needs, and emerging industry trends
- Established the overall product security direction and risk management framework for the enterprise, ensuring the consistent and safe operation of products
- Defined the product cybersecurity development and reference architecture framework while managing traceability between business strategy and cybersecurity
- Provided technical guidance for security control capabilities, encompassing both first-party and third-party cloud environments as well as traditional MSP/outsourced IT setups
- Worked in cooperation with the Product Engineering teams to incorporate enterprise security capabilities and industry security regulatory requirements into product and connected service architecture
- Acted as an escalation point for product security architecture decisions that spanned multiple business divisions or involved interoperability and data exchange with third-party systems
- Led a team responsible for conducting routine product security, interoperability, and architecture risk assessments and threat modeling exercises
- Participated in major new product development projects to ensure the integration of appropriate security controls
- Established security standards and processes for assessing vendors and suppliers directly impacting product design, operation, and safety
- Played a key role in designing, monitoring, and optimizing product security controls for safeguarding information assets and sensitive data in cloud-based solutions, including IaaS, PaaS, and SaaS
- Managed services for security monitoring, identity, and access management, and data protection from managed service providers (MSP) and cloud-based solutions
- Formulated and implemented strategic changes to enhance quality, productivity, and employee satisfaction
- Contributed to meeting the sales and profitability requirements of the business as outlined in the strategic plans
- Evaluated the success of the organization in achieving budgeted, planned, and targeted goals
Quality Assurance Analysts
Computer and Information Technology (IT) · June, 2004 - June, 2005
Roles & Responsibilities
- Facilitated meetings with business owners to meticulously gather project requirements, ensuring a comprehensive understanding of their needs
- Crafted business and technical requirements tailored specifically for web-based applications, aligning them with project objectives and constraints
- Took charge of creating comprehensive Business Requirements Documents, providing a detailed blueprint for project development and validation
- Developed and implemented the overall Test Strategy, Test Plans, and meticulously detailed Test Cases based on the identified business and system requirements
- Demonstrated proficiency in crafting and executing automated test scripts using the functional testing tool Mercury Win Runner, streamlining the testing process for efficiency and precision
- Assumed responsibility for effectively managing and meticulously documenting Requirements, Test Cases, and Defects using the Test Management tool, Mercury Test-Director, ensuring a structured and organized testing environment
- Conducted rigorous testing activities, including thorough User Interface validation, Functionality testing to validate system features, and Regression testing to ensure ongoing system integrity
- Carried out Load and Stress testing using specialized tools like Mercury Load Runner, evaluating the application's performance under varying levels of stress and load and addressing performance bottlenecks as necessary
Skills
- QRadar
- ArcSight
- RSA SA
- McAfee Nitro
- Splunk
- Azure Sentinel and Securonix
- FireEye HX
- FireEye AX (Sandboxing)
Education
Indira Gandhi Open University
Computer Science
2002-2004
Want Shailendra for your Next Training?
Request a DemoOther Trainers
Mehak
First Time Managers Trainer in Bangalore
14+ years of Experience
Oyiboka
Project Management Trainer in Abuja
11+ years of Experience
Ravi
Change Management Trainer in Bangalore
12+ years of Experience
Satyanarayana
Cybersecurity Fundamentals Trainer in Hyderabad
7+ years of Experience

Nibedita
Motivational Skills Trainer in Bangalore
9+ years of Experience

Roberta
Self Awareness Trainer in Al Wajba
11+ years of Experience
Venu
MongoDB Trainer in Hyderabad
19+ years of Experience
Mrinal
Personality Development Trainer in Gurgaon
22+ years of Experience

Harshil
First Aid and CPR Trainer in Ahmedabad
10+ years of Experience
Yogesh
Team Building Trainer in Delhi
14+ years of Experience

Simon
Self Awareness Trainer in Ubud
9+ years of Experience

Tamer
Cost Reduction in Procurement Trainer in CAIRO
19+ years of Experience
More Corporate Training Programs
- Employee Experience (EX) Design & Measurement Training
- AI and LLM Observability Corporate Training
- Data Mesh & Streaming Architecture Training
- PostgreSQL Performance Tuning Training
- Platform Engineering & Internal Developer Platforms Training
- Micro-Frontends Architecture Corporate Training
- LangChain & LLM Application Development Training
- Human Factors Engineering Training