
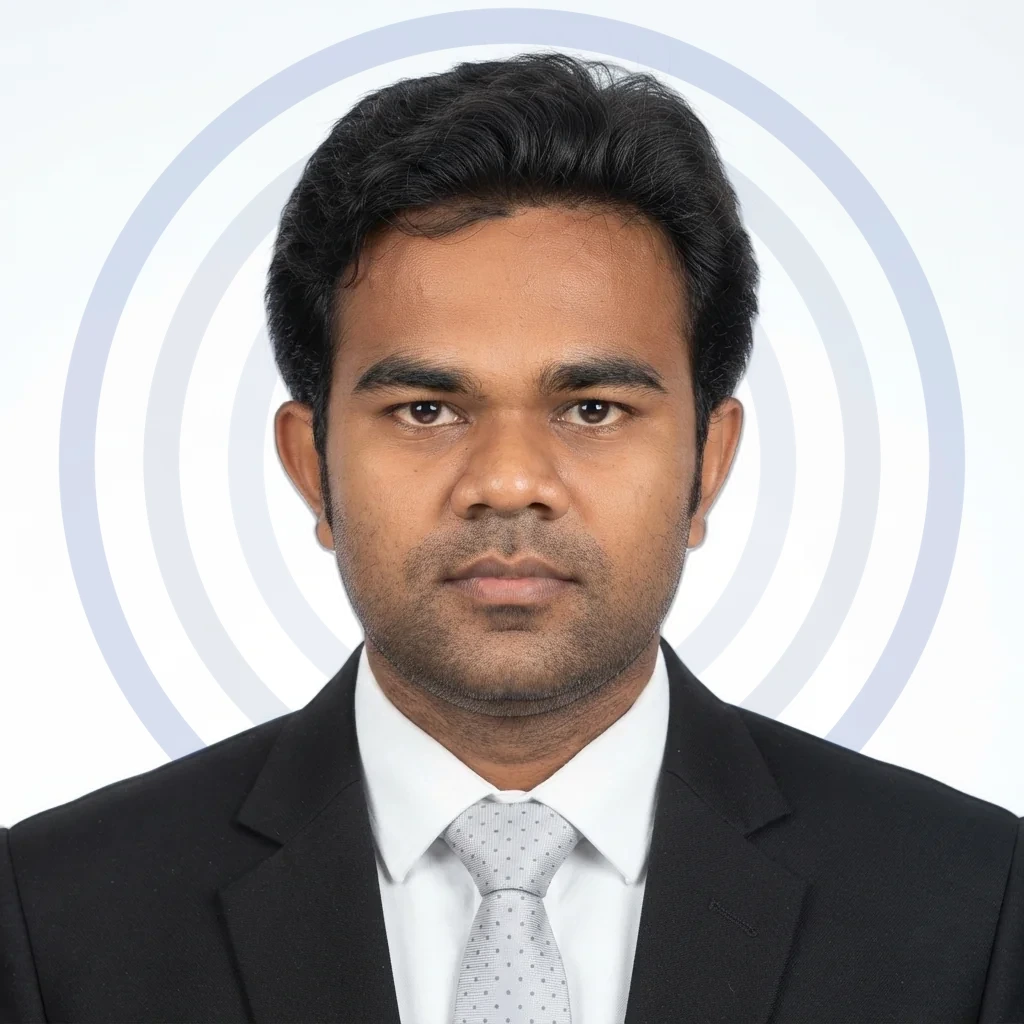
Shitanshu
Certified Ethical Hacker (CEH) Trainer in Pune
- CEH (Certified Ethical Hacker)
- Certified Information Security Manager (CISM)
- Certified in Risk and Information Systems Control (CRISC)
- Location
- Pune, India
- Trainer Since
- March, 2008
Certified Ethical Hacker (CEH) Trainer in Pune
About Shitanshu
Shitanshu is a seasoned and highly accomplished Cyber Security Leader with over 18 years of extensive experience in the field. With a remarkable skill set encompassing various domains, he has become a prominent figure in information security. As an authoritative speaker, he has shared his profound knowledge at numerous conferences and seminars, enlightening audiences about the ever-evolving landscape of cyber threats and strategies to combat them. His expertise in governance risk & compliance management and SOC management has proved invaluable to organizations seeking to fortify their digital defenses.
Not only is Shitanshu a visionary in cyber security, but he is also an accomplished author who has penned several influential publications, contributing to the collective understanding of the subject. His role as an ADP (Accelerated Development Programme) expert further exemplifies his dedication to safeguarding critical systems and data from potential cyber-attacks. Beyond his technical prowess, he has also honed his skills as a Security Solution Architect, devising innovative and robust security measures for diverse business environments.
Moreover, Shitanshu's focus on privacy and digital transformation underscores his commitment to ensuring data protection while embracing the advancements of the digital era. Through his comprehensive training programs, he has empowered countless professionals to take on cyber security challenges with confidence and competence, leaving an indelible mark on the industry.
Shitanshu is a Corporate Trainer For
CEH (Certified Ethical Hacker)
Training Since:March, 2008
Certified Information Security Manager (CISM)
Training Since:September, 2021
Certified in Risk and Information Systems Control (CRISC)
Training Since:October, 2022
Work Experience
Global Cybersecurity Architect
Computer and Information Technology (IT) · May, 2022 - present
Roles & Responsibilities
- Designing and implementing cutting-edge security frameworks and measures to protect global IT infrastructures and systems from evolving cyber threats
- Collaborating with cross-functional teams to develop and maintain a robust incident response plan, ensuring prompt detection and mitigation of security breaches
- Conducting ongoing vulnerability assessments and risk analyses to identify potential weaknesses and proactively address security loopholes
- Continuously researching emerging cyber threats and trends to inform the development of proactive security strategies and countermeasures
- Defining and enforcing security policies, standards, and procedures across the organization to ensure consistent adherence to best practices
- Providing technical leadership and guidance to security teams worldwide, fostering a culture of security awareness and knowledge sharing throughout the organization
Director - Security Engineering Operations & Compliance
Computer and Information Technology (IT) · July, 2015 - February, 2022
Roles & Responsibilities
- Directed the security engineering operations & compliance team, overseeing their day-to-day activities and ensuring alignment with organizational goals
- Led efforts to achieve and maintain compliance with relevant industry standards and regulations, such as ISO 27001, GDPR, and HIPAA, through rigorous audits and assessments
- Collaborated with cross-functional teams, including IT, legal, and risk management, to establish security policies and procedures, promoting a culture of security awareness and accountability
- Spearheaded the design and deployment of advanced security tools and technologies, including SIEM solutions, intrusion detection systems, and threat intelligence platforms, to enhance the organization's overall security posture
- Conducted regular performance evaluations, provided mentorship, and facilitated professional development opportunities for team members, fostering a highly skilled and motivated security engineering workforce
Global Security Operations Manager
Banking, Financial Services and Insurance · January, 2014 - July, 2015
Roles & Responsibilities
- Oversaw and managed the Global Security Operations team, ensuring 24/7 monitoring and response to security incidents across the organization's worldwide operations
- Established and maintained standard operating procedures for incident detection, analysis, and resolution, optimizing the team's efficiency and effectiveness in handling security events
- Collaborated with internal stakeholders, external vendors, and law enforcement agencies to investigate and mitigate security breaches, minimizing the impact on business operations
- Implemented and maintained security technologies, such as IDS/IPS, firewalls, and endpoint protection, to fortify the organization's infrastructure and data against cyber threats
- Conducted regular security awareness training for employees, promoting a security-conscious culture and empowering them to recognize and report potential security risks
- Prepared and presented comprehensive security reports and metrics to senior management, providing insights into the organization's security posture and recommending improvements to security strategies and measures
SOC Professional
Computer and Information Technology (IT) · December, 2013 - July, 2015
Roles & Responsibilities
- Monitored security alerts and events within the Security Operations Center (SOC), investigating and analyzing potential security incidents to determine their nature and severity
- Assisted in the deployment, configuration, and maintenance of security technologies, including SIEM, firewalls, and intrusion detection systems, to ensure optimal performance and threat detection capabilities
- Collaborated with incident response teams to contain and mitigate security breaches, following established protocols and procedures to minimize the impact on the organization
- Conducted periodic vulnerability assessments and penetration tests to identify weaknesses in the organization's systems and applications, providing valuable insights for remediation efforts
- Participated in security incident handling and response exercises, honing incident response skills and contributing to continuously improving the SOC's incident response capabilities
- Documented all security-related activities, incident reports, and investigation findings, maintaining accurate records for future reference and regulatory compliance purposes
Skills
- Technology Compliance
- Governance Risk and Compliance
- Negotiation Skills
- Firwalls
- VPN
- Network Engineering
- Penetration Testing
- IT Service Management
- Computer Forensics
- Vendor Management
- Team Management
- Strategic Leadership
- Content Security
- SOC
Education
MakhanLal Chaturvery Rashtriya Patrakarita Vishwavidyalaya
Computer Application
2000-2003
DOEACC, New Delhi
Computer Application
2005-2009
Symbiosis Centre for Management Studies
Business Administration, Management and Operations
2014-2017
Projects
Evangelised the Secops Products and made it Cloud native/SAAS
May 2022 - May 2023
Want Shitanshu for your Next Training?
Request a DemoOther Trainers
Mehak
First Time Managers Trainer in Bangalore
14+ years of Experience
Oyiboka
Project Management Trainer in Abuja
11+ years of Experience
Ravi
Change Management Trainer in Bangalore
12+ years of Experience
Satyanarayana
Cybersecurity Fundamentals Trainer in Hyderabad
7+ years of Experience

Nibedita
Motivational Skills Trainer in Bangalore
9+ years of Experience

Roberta
Self Awareness Trainer in Al Wajba
11+ years of Experience
Venu
MongoDB Trainer in Hyderabad
19+ years of Experience
Mrinal
Personality Development Trainer in Gurgaon
22+ years of Experience

Harshil
First Aid and CPR Trainer in Ahmedabad
10+ years of Experience
Yogesh
Team Building Trainer in Delhi
14+ years of Experience

Simon
Self Awareness Trainer in Ubud
9+ years of Experience

Tamer
Cost Reduction in Procurement Trainer in CAIRO
19+ years of Experience
More Corporate Training Programs
- Employee Experience (EX) Design & Measurement Training
- AI and LLM Observability Corporate Training
- Data Mesh & Streaming Architecture Training
- PostgreSQL Performance Tuning Training
- Platform Engineering & Internal Developer Platforms Training
- Micro-Frontends Architecture Corporate Training
- LangChain & LLM Application Development Training
- Human Factors Engineering Training