
Zero Trust Security Corporate Training
Design identity-centric access, segment networks, and enforce continuous verification across your estate.
Your security and network teams learn to adopt zero trust end to end. Employees design identity-based access policies, build micro-segmentation, enforce device trust, and operate policy engines with continuous monitoring. Every module pairs concepts with guided labs, so your team practices zero trust architecture on realistic environments and leaves ready to roll it out.
Instructor-led group trainingVirtual / on-site / off-site10 languagesDelivered inEnglish, Spanish, Mandarin, German, Arabic, Portuguese, Hindi, French, Japanese, Italian100+ countriesWe have delivered inUnited States, United Kingdom, India, Canada, Germany, France, Netherlands, UAE, Saudi Arabia, Singapore, Australia, Japan, Brazil, South Africa and 90+ more countries
How we build a zero trust-ready security team
EDSTELLAR CYBERSECURITY CAPABILITY MODEL
Assess trust boundaries
Skill checks map your team's identity, segmentation, and policy maturity.
Set shared access standards
One shared playbook for identity policies, segmentation, and review.
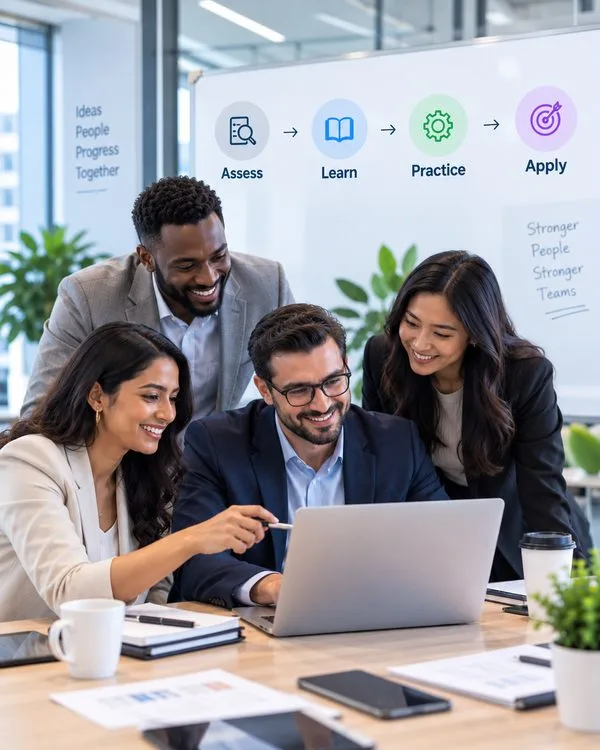
Practice in guided labs
Labs cover identity perimeters, micro-segmentation, and device trust.
Measure the lift
Lab reviews benchmark each engineer's zero trust design capability.
Scale across teams
One standard rolls out across network, identity, and SOC functions.





Need more than one program?Get a group quote
Trusted as a Leading Corporate Training Provider by
















Program Overview: What is Zero Trust Security?
Zero Trust Security is Edstellar's instructor-led program for security, network, and endpoint teams replacing implicit trust with verified access. It covers zero trust foundations and the five pillars, identity as the security perimeter, network and micro-segmentation, device trust and compliance, and policy engines with continuous monitoring. Teams assess their current trust posture and practice the techniques module by module.
Training runs across six modules in 24 instructor-led hours, pairing every concept with a guided lab. Your team practices conditional access configuration, least-privilege role design, micro-segmentation mechanics, device compliance gates, and policy tuning with live telemetry. Instructors adapt the exercises to your identity providers, network zones, and endpoint mix, coaching access decisions on realistic enterprise traffic. The capstone is a rollout exercise: the team phases identity, network, and device rollouts, plans migration without disruption, and presents the architecture and roadmap.
Teams that defend a hard perimeter while everything valuable lives in the cloud fight an architecture the business already outgrew. VPN hairpins, unmanaged devices, and all-or-nothing access slow people down without stopping determined attackers. This program teaches your team to make identity the perimeter, segment the network so breaches stay contained, and enforce policy on every access attempt.
The capstone ends with the team presenting their own enterprise's zero trust rollout to a review panel: the trust-posture assessment that exposes where the organization really stands, phased identity, network, and device plans sequenced for migration without business disruption, and the architecture and roadmap document that justifies each phase. Defending those choices out loud, against questions, is the real outcome; the team returns ready to argue the rollout in a real boardroom.
Six modules and 24 hours: zero trust foundations, identity as the perimeter, network segmentation and micro-segmentation, device trust and endpoint compliance, and policy engines with continuous monitoring. Every module pairs concepts with a guided lab, so each technique is practiced. It closes with a capstone zero trust architecture rollout the team designs against a realistic enterprise environment.
What's Included in this Workshop for Your Enterprise Teams
- 1
Zero trust principle briefings
Internalize never-trust, always-verify design thinking.
- 2
Identity policy workshops
Design least-privilege access around identity.
- 3
Segmentation labs
Build micro-segmentation in realistic network labs.
- 4
Device trust exercises
Enforce endpoint compliance before granting access.
- 5
Capstone rollout design
Architect a phased zero trust rollout as a team.
- Instructor-led delivery across virtual, onsite, and hybrid
- Guided labs in every module with instructor coaching
- Capstone zero trust architecture rollout
- Flexible scheduling around your calendar
- Lab guides and reusable templates included
- Group size and batches set along with you
Build your team's skills. Anywhere in the world.
Real-world use cases
from day one
Instructor-led training
for your teams
Delivered globally
in 100+ countries

Enterprise Training Solutions Customized for Your Company
One partner for instructor-led corporate training, delivered the way your teams work.
Request a Training Quote- Customized Training Delivery
- Scale Your Training: Small to Large Teams
- In-person Onsite, Live Virtual or Hybrid Training Modes
- Plan from 2000+ Industry-ready Training Programs
- Hands-On Labs on Live Infrastructure, Led by Industry Experts
Zero Trust Security Course Topics and Program Outline
Six modules take your team from zero trust fundamentals to a capstone architecture rollout, with guided labs in every module.
Built by Edstellar with zero trust architects
Built by practitioners who design and operate zero trust architectures in production, shaped around your stack and use cases.
Skill checks baseline your team's identity, network segmentation, and access policy maturity before training begins.
Live instruction covers zero trust principles, pillars, and reference models across 3.5 focused hours.
Guided labs build identity policies, segmentation rules, and device trust checks across 8 hours of supervised practice.
Your team designs a phased zero trust rollout in a 5-hour capstone, reviewed against architecture standards.
From zero trust fundamentals to a capstone rollout design, every control is practiced in guided labs.
Delivered as
Delivered as a hybrid program of live instruction and guided labs, scheduled around your team's calendar in flexible batches.
Map trust boundaries across a sample enterprise environment.
learna)Never trust, always verify: core principles
b)The five pillars of zero trust
c)Reference models and maturity stages
d)Assessing your current trust posture
Build least-privilege identity policies in a guided lab.
practicea)Identity providers and strong authentication
b)Conditional access policies that adapt to risk
c)Least-privilege role and entitlement design
d)Privileged identity safeguards
Segment a lab network and verify east-west traffic controls.
practicea)Segmentation strategy and zone design
b)Micro-segmentation policy mechanics
c)Software-defined perimeters in practice
d)Validating east-west traffic controls
Enforce device compliance gates in access decisions.
applya)Device identity and health attestation
b)Compliance gates in access decisions
c)Managing BYOD and unmanaged devices
d)Remediation workflows for non-compliant devices
Tune policy decisions and monitoring for access anomalies.
applya)Policy decision and enforcement points
b)Telemetry for access decisions
c)Analytics for anomalous access patterns
d)Tuning policies without blocking work
Design a phased zero trust rollout and defend it in review.
applya)Assessing the enterprise trust posture
b)Phasing identity, network, and device rollouts
c)Migration without business disruption
d)Presenting the architecture and roadmap
Customize this program tailored to your team?
Tell us your training needs: what your team already works with, the level they’re at, and the topics you want them to focus on. We’ll adjust the modules, duration and hands-on labs, and send you a customized outline for your group.
Key Skills and Outcomes Your Team Will Gain
Seven job-ready outcomes your team will demonstrate by the end of the program. Each competency is practiced in guided labs and reviewed in the capstone rollout.
Explain zero trust principles
Describe the pillars, maturity stages, and mindset shift behind never-trust, always-verify.
Design identity-centric policies
Build conditional, least-privilege access policies anchored on strong identity.
Segment networks with micro-segmentation
Design zones and enforce east-west traffic controls that contain lateral movement.
Enforce device trust
Gate access on device health and compliance, including BYOD and unmanaged endpoints.
Operate policy engines
Run policy decision points and tune enforcement without blocking legitimate work.
Monitor access continuously
Use telemetry and analytics to verify every access decision on an ongoing basis.
Lead a zero trust rollout
Phase identity, network, and device workstreams into a defensible rollout roadmap.
Teams that Benefit from this Zero Trust Security Group Training
This group training is built for security, network, and identity teams replacing perimeter defense with continuous verification. Content adapts to each cohort's roles, stack, and experience, so every batch practices the workflows it owns, from identity policy design to segmentation rollout.
Segment the network without breaking it.
Learn segmentation patterns that contain threats while keeping applications reachable and performant.
Workflow friction
- Flat network sprawl
- Untested segmentation rules
- Fear of breaking connectivity
How the program helps
- Contained lateral movement
- Verified east-west controls
- Resilient zone design
Practice use cases
- Segmentation labs
- Traffic validation
- Zone design reviews
Make identity the perimeter.
Design conditional, least-privilege access that adapts to risk signals in real time.
Workflow friction
- Over-permissioned roles
- Weak conditional signals
- Privileged access sprawl
How the program helps
- Risk-aware access policies
- Stronger authentication posture
- Cleaner entitlement models
Practice use cases
- Policy design labs
- Entitlement reviews
- MFA rollout drills
Design policy-driven access.
Architect the decision points, telemetry, and governance that make zero trust enforceable.
Workflow friction
- Vague zero trust roadmaps
- Disconnected tooling
- Unmeasured progress
How the program helps
- Enforceable access architecture
- Clear rollout phasing
- Measurable trust posture
Practice use cases
- Architecture workshops
- Roadmap planning
- Maturity assessments
Monitor every access decision.
Turn access telemetry into detections and run response playbooks for identity-driven attacks.
Workflow friction
- Blind spots in access logs
- Noisy identity alerts
- Slow cross-team handoffs
How the program helps
- Identity-aware detections
- Faster access anomaly triage
- Coordinated incident response
Practice use cases
- Detection labs
- Anomaly hunts
- Response simulations
Cohorts train as a cross-functional workforce, with each small group aligned on shared access and review standards.
Prerequisites: This program benefits network engineers, identity teams, security architects, and SOC analysts moving toward zero trust. Basic networking and identity concepts help but are not required. Content adapts to each cohort's tools, environment, and maturity.
Network Engineer to Zero Trust Architect
Tracks how practitioners progress from zero trust fundamentals to leading phased rollouts across the program's learn, practice, and apply phases.
A program that grows with security careers, from first zero trust concepts to confident leadership of enterprise rollouts.
Different Teams, Locations, Time Zones, or Languages? We've Got You Covered.
Whether your teams are spread across countries, time zones, languages, or experience levels, we deliver tailored training programs that ensure a consistent learning experience across your global workforce.
Certificate of Training Completion.
On successful completion, employees receive an Edstellar course completion certificate, recognizing their commitment to ongoing learning and professional development. It validates the skills they have built and motivates them to keep growing and contribute to organizational success.
Earned, not attended. Awarded on completion of all hands-on labs and the capstone project.

Training Delivery Modes: Onsite, Virtual and Hybrid
Live instruction with guided labs in every module, available across onsite, virtual, and hybrid formats to fit your team's schedule.
Onsite Training
Instructor-led training at your offices, with labs set up on your network and tooling. The instructor works alongside the team in segmentation labs and the capstone rollout design.
- Instructor-led training at your offices
- Labs set up on your network and tooling
- In-person coaching and reviews
- Exercises tuned to your network and identity stack

Live Virtual Training
Live virtual sessions on Zoom or Teams with screen-shared walkthroughs, breakout labs, and real-time reviews. Your team gets the same guided labs and capstone rollout from anywhere.
- Live virtual sessions on Zoom or Teams
- Screen-shared walkthroughs and breakout labs
- Real-time review with the instructor
- Same guided labs as onsite, from anywhere

Hybrid Training
Instructor-led sessions mix onsite and virtual delivery with guided labs throughout. Teams practice identity policy design, segmentation, and device trust with coaching at every step.
- Live instruction across onsite and virtual sessions
- Guided labs with instructor coaching and reviews
- Real zero trust workflows with hands-on practice
- Flexible scheduling without losing live interaction

Need a customized training format that works for your team?
Our training delivery is customized to your team's schedule, full days, half days, sessions spread across weeks, or modular formats. Share your preferred timeline, and we'll plan the training around it.
Frequently Asked Questions
Share your team size, timelines, and delivery preference, and we will send a detailed per-group quote with batch options.
Yes. Book a discovery call and we will map your network, identity stack, and maturity to a tailored training plan.
Yes. Live virtual sessions run on Zoom or Teams with the same guided labs and instructor coaching as onsite delivery.
Yes. The instructor runs the full program at your offices, with labs set up on your network and tooling.
The program runs 24 hours across six modules, closing with a 5-hour capstone zero trust architecture rollout.
Question not answered here?
Put it in the request. A training specialist answers it directly, within one business day.
Where this Training Fits in Your Team's learning path.
Zero trust comes after identity management and network segmentation, because it combines both: verify every user and device, and limit what they can reach. Once the model is designed, SASE is how many organisations deliver it to remote users and branches.
IDENTITY BASICS
Identity & Access Management Training
Set up authentication, MFA and identity lifecycle, the first signal zero trust checks.
SEGMENT THE NETWORK
Enterprise Network Security & Segmentation Training
Divide the network into zones, so access can be limited to what is needed.
ADOPT ZERO TRUST
Zero Trust Security Training
Design and roll out a zero trust model using identity, device posture and least privilege.
MOVE TO SASE
SASE, SD-WAN & Zero Trust Network Access Training
Deliver zero trust access to remote users and branches through SASE and ZTNA.
Why Choose Edstellar as Your Zero Trust Security Corporate Training Provider
When comparing providers, Edstellar is the training partner teams choose for zero trust expertise and 5+ years of corporate training experience. Our method pairs briefings with guided labs, so capability is demonstrated, not just described.
EXPERT TRAINERS
YEARS DELIVERING
ORGANIZATIONS TRAINED
CERTIFIED
Tailored
Every cohort's labs, examples, and exercises are tuned to your identity providers, network zones, and device fleet.
Proven Methodology
A learn, practice, apply arc moves your team from zero trust concepts to a live capstone rollout design.
Practice-Based Learning
Guided labs in every module build identity policy design, segmentation, and device trust skill.
Expert Trainers
Practitioners who run zero trust architectures in production lead every session.
Global Scale
One consistent program rolls out across network, identity, and SOC teams in every region.
Measurable Outcomes
Lab checkpoints and the capstone review show exactly how far your zero trust posture has advanced.
Design Zero Trust Access With Explicit Identity, Device, and Policy Evidence
Edstellar develops zero trust capability by replacing broad assumptions with reviewable access decisions. Participants connect identity controls, segmentation, device compliance, and policy engines before examining continuous monitoring. A phased architecture rollout demonstrates how these components work together, with feedback on least privilege, verification signals, and the practical dependencies behind implementation priorities.
- Step 01
Consult
We explore security and infrastructure responsibilities, identifying gaps in implicit trust assumptions, identity permissions, network boundaries, device posture, and monitoring of changing access risk.
- Step 02
Plan
We establish zero trust principles, develop identity and segmentation controls, then connect device trust and policy decisions with continuous monitoring and a phased rollout design.
- Step 03
Align
We align security architecture expertise with identity, network, endpoint, and SOC teams, clarifying shared responsibilities and calibrating exercises to networking and access-control experience.
- Step 04
Customize
We adapt a fictional application estate and user-device scenarios to familiar access needs, preserving policy exceptions and anomalous behavior without changing live privileges or collecting employee activity.
- Step 05
Execute
Participants design least-privilege policies, segment sample workloads, and tune monitored access decisions, receiving feedback on verification signals, rule consistency, exception handling, and operational dependencies.
- Step 06
Evaluate
We assess the rollout for justified trust boundaries, coherent identity and device checks, meaningful monitoring, and a practical sequence that makes policy ownership and unresolved dependencies explicit.
Also from Edstellar
Talent assessments
Psychometric, behavioral, leadership and 360-degree assessment.
→Training needs analysis
Needs analysis, gap identification, and a training roadmap.
→L&D consulting
Learning strategy, content, technology and ROI measurement.
→OD consulting
Org design, succession planning and cultural change.
→Managed training services
Training outsourcing, vendor management, logistics and administration.
→Coaching solutions
Executive and manager coaching that keeps skills in use.
Start an RFP shaped to your needs.
Answer three quick questions about team size, scope, and how often you need the program run, then send the request from the last step. Everything you choose travels with it, so you only fill this in once.
How many team members need training?
Zero Trust Security Training Packages & Pricing
Where L&D holds an annual budget, license packages price the whole year at once instead of raising a purchase order per workshop. Hours and licenses are pooled across teams, programs and locations, so unused capacity is not stranded in one department.
Starter
120
trainee licenses64 hours of group training
Tailored for SMBs
Growth
320
trainee licenses160 hours of group training
Ideal for growing SMBs
Enterprise
800
trainee licenses400 hours of group training
Designed for large corporations
Custom
Unlimited
trainee licensesDuration set by the rollout
Multi-region and multi-year
Training Packages & Pricing
Choose the training format that works for your team. Pricing is customized based on your requirements, cohort size, and delivery needs.
Request a Quote for Zero Trust Security Training for Your Team
Share your team size, identity and network stack, maturity stage, and timelines to receive a tailored training plan and quote. Book a discovery call to discuss your goals.